Most independent fitness coaches are not covered by HIPAA. HIPAA applies when you work for or receive protected health information from a covered entity, or when your services make you a business associate under federal rules. Even outside HIPAA, consumer-facing apps and trackers can still trigger separate duties under the FTC Health Breach Notification Rule.
TL;DR:
- Most independent fitness coaches who do not bill insurance or handle client health data from healthcare providers are not subject to HIPAA regulations.
- When a coach receives protected health information from clinics, providers, or health plans, or shares PHI with them, HIPAA obligations, including breach reporting and safeguards, automatically apply.
- The FTC Health Breach Notification Rule also requires health apps and tracking tools to notify users and authorities of data breaches, regardless of HIPAA coverage.
- Implementing a data mapping, risk analysis, technical controls, consent language, and a breach response plan is essential for legal protection and privacy management.
- Coaches should consider state-specific privacy laws and use centralized, secure coaching platforms to support compliance efforts effectively.
What HIPAA covers and how to tell if you’re a covered entity
HIPAA Rules apply only to covered entities and their business associates. Covered entities are health plans, health care clearinghouses, and health care providers who conduct standard electronic transactions, such as billing insurance for services. An independent personal trainer or online coach who takes payment directly from clients and does not bill insurance typically falls outside that definition.
The HIPAA framework has three operating parts. The Privacy Rule limits how covered entities use and disclose health information. The Security Rule requires administrative, physical, and technical safeguards for electronic health data. The Breach Notification Rule sets deadlines for reporting exposures of unsecured protected health information (PHI).
Three questions settle most coverage questions:
- Do you bill health insurance or process standard electronic health care transactions?
- Does a doctor, clinic, or health plan send you client health data as part of a formal arrangement?
- Do you store or transmit health records on behalf of a provider or plan?
A “no” to all three generally means HIPAA does not apply to your coaching practice directly.
When a coach becomes a business associate: concrete scenarios
Coverage changes the moment you start handling PHI for someone else’s covered entity. A business associate is a person or organization that performs services involving PHI on behalf of a covered entity, or receives PHI from one in the course of that work. Common scenarios include:
- A physical therapy clinic refers patients to you and shares their treatment notes.
- An employer’s group health plan hires you to run a wellness program tied to plan eligibility or incentives.
- You integrate your intake process with a provider’s electronic health record system.
- A client’s doctor sends you lab results or a medical clearance directly, at your request.
Once you fit any of these, HIPAA obligations follow. Business associates are directly liable for Security Rule compliance and must report breaches of unsecured PHI to the covered entity without unreasonable delay, no later than 60 days after discovery. That liability exists independent of whether the covered entity catches the issue first.
The operational response is straightforward: never accept PHI from a clinic or health plan without a signed Business Associate Agreement (BAA) in place first, and vet any software vendor you use for that work the same way a covered entity would vet you.

Pro Tip: If a referral partner offers to “just send over the client’s file,” pause and get a BAA signed before you say yes.
FTC rules on health apps, trackers and consumer tools
HIPAA is not the only federal privacy regime coaches need to track. The FTC Health Breach Notification Rule requires vendors of personal health records and related entities that fall outside HIPAA to notify affected users and the FTC when unsecured, identifiable health information is breached. The 2024 amendments clarified that this applies to health apps and connected devices, not just traditional medical record vendors.
This matters for coaching tools that sync data from multiple sources, such as a wearable, a nutrition log, and a coaching app feeding into one client profile. Feature design, specifically whether a tool draws health data from more than one source, often determines FTC coverage more than the size of the business running it.
Practical consequences include:
- Breach notification obligations to users and the FTC, separate from any HIPAA duty.
- Civil penalties for noncompliance with notification requirements.
- A need to document what health data categories your tools actually collect and sync.
Practical compliance checklist coaches can implement today
A short checklist gets you most of the way to a defensible privacy posture, with or without HIPAA coverage.
- Map your data. List every place client health information lives: intake forms, chat threads, spreadsheets, apps.
- Identify BAA triggers. Flag any relationship with a clinic, plan, or provider that sends or requests PHI.
- Run a basic risk analysis. Note where data is weakest: unencrypted files, shared logins, unsecured messaging.
- Apply technical controls. Multifactor authentication, encryption in transit and at rest, and role-based access limit exposure if a device or account is compromised.
- Write consent and retention language. State clearly what health data you collect, why, and how long you keep it.
- Build a breach playbook. Know who you notify, how fast, and what you say, before an incident happens.
Breach notification rules under HHS require covered entities and business associates to notify affected individuals and the Secretary without unreasonable delay, generally no later than 60 days for large breaches. That 60-day clock starts at discovery, not at confirmation of the full scope, so a documented playbook saves time you do not have once an incident is underway.
Pro Tip: Store your consent forms and intake data in one secure, access-controlled system rather than scattered across email and spreadsheets.
Document every risk assessment, staff training session, and vendor review in writing. If a client, partner, or regulator ever asks what safeguards you had in place, the paper trail matters as much as the safeguard itself.
State and other non-HIPAA obligations
HIPAA is a floor, not the whole picture. State breach-notification and consumer privacy statutes can apply to coaches who are never covered by HIPAA at all, and requirements vary significantly by state. Some states require notification within a fixed number of days of discovery, others set no fixed deadline but demand “without unreasonable delay,” and definitions of what counts as personal information differ.
If you coach clients across state lines or run an online practice, adopting the strictest applicable standard, meaning encryption, documented consent, and BAAs wherever PHI changes hands, simplifies compliance more than trying to track every state’s rules individually. Keep records of consent language and any data requests you receive, since response timelines for those requests also vary by jurisdiction.
How coaching software supports these safeguards
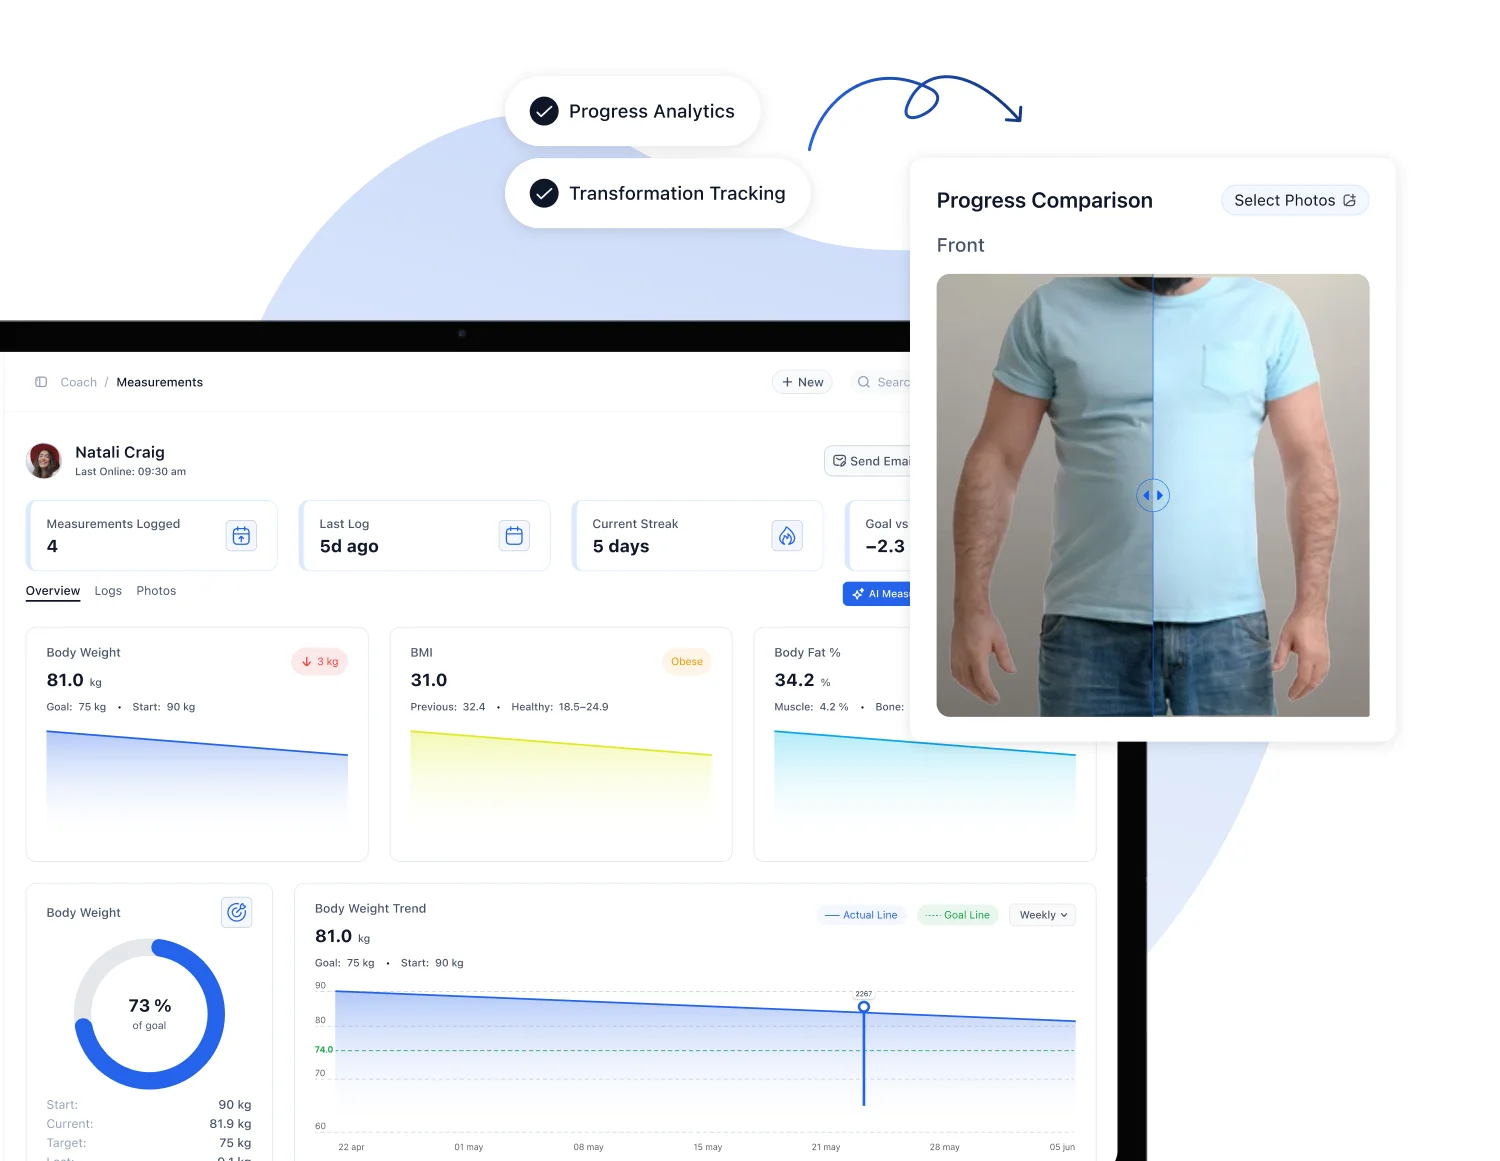
Coaching platforms can help operationalize several items on the checklist above. Centralizing intake forms, consent language, and client notes in one client portal reduces the scattered-spreadsheet problem that makes data mapping hard in the first place. Role-based logins limit which staff members can see sensitive client fields, and calendar sync with Google Calendar or Microsoft Outlook and Microsoft 365 keeps scheduling data inside controlled systems rather than exported into shared calendars. Public API access is available for coaches connecting coaching workflows to other tools.
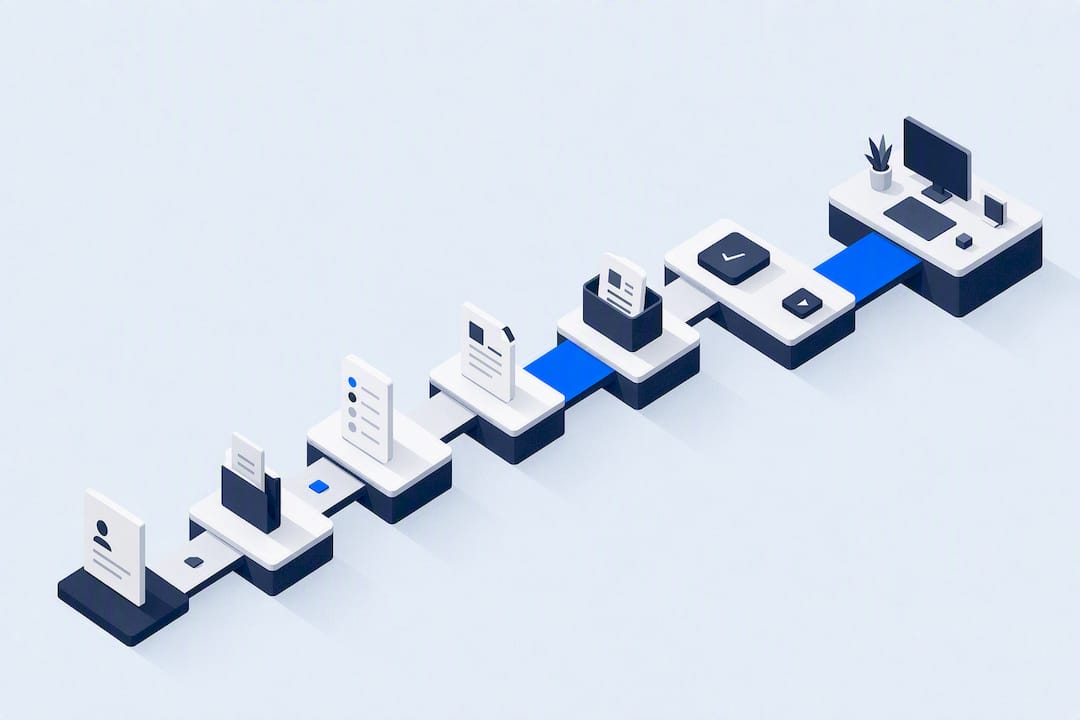
A typical workflow looks like this: a client completes an intake and consent form inside the secure portal, a coach with limited role-based access reviews it, and any later incident investigation can rely on activity logs tied to that record rather than guesswork. As community-driven fitness software, these features are developed based on feedback from working fitness professionals, though not every requested feature becomes part of the product. Confirm current integrations and setup details on the FITsociety calendar page before relying on them, and remember that legal responsibility for compliance stays with you as the coach, not with any software vendor.
If centralizing client intake, consent records, and scheduling sounds like the gap in your current setup, FITsociety’s coaching tools are built around exactly that kind of workflow, from secure intake through ongoing nutrition and training delivery with the nutrition software for online coaches. Plans start at $179 per month for the Coach tier, covering up to 100 members and two coaches, with higher tiers available for larger teams. Check current pricing and plan details on the FITsociety pricing page before signing up.
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.

FAQ
Does HIPAA apply to personal trainers by default?
No. HIPAA applies only to covered entities and their business associates, and most independent personal trainers who bill clients directly do not meet that definition. You become subject to HIPAA only when you take on a role like a business associate for a clinic, plan, or provider.
What counts as protected health information in coaching?
In a coaching context, PHI typically means health data tied to an identifiable person that comes from or is shared with a covered entity, such as a doctor’s note, a medical clearance, or insurance-linked wellness data. General fitness logs a client enters voluntarily, like workout history or body measurements, are not automatically PHI unless they originate from a covered entity relationship.
What happens if I receive client health records from a doctor?
If you proactively request or receive official medical records from a provider rather than having a client share their own notes, you become a recipient of PHI and should treat that relationship with HIPAA-level care. That means obtaining proper authorization and putting a Business Associate Agreement in place with the provider before the data changes hands.
Are fitness apps and trackers covered by HIPAA?
Usually not directly, but many fall under the FTC Health Breach Notification Rule instead, which covers vendors of personal health records and related tools outside HIPAA’s scope. Apps that sync health data from multiple sources are more likely to trigger this rule than single-purpose tracking tools.
How fast must a breach be reported under HIPAA?
Covered entities and business associates must notify affected individuals and the HHS Secretary without unreasonable delay, generally no later than 60 days after discovering a breach of unsecured PHI. Additional media notification requirements apply for large breaches within the same window, as detailed in the official HHS breach notification guidance.
Sources
- HHS — HIPAA Privacy Rule and Overview
- FTC — Health Breach Notification Rule basics for business